


It sounds like yet another headline from the COVID-19 pandemic chronicles, but this time it is about a digital pandemic and the fever over personal data protection.
The largest personal data theft in the history of independent Lithuania has opened Pandora’s box: businesses invest too little in infrastructure and data security and take on too much risk, because the “IT security” line is the easiest one to cut sharply or delete from annual budgets. Almost nobody understands what it is, and those who really do cannot prove to management that the risk is real and that very serious problems can arise practically at any time.
No need to be afraid and wait – you need to act.
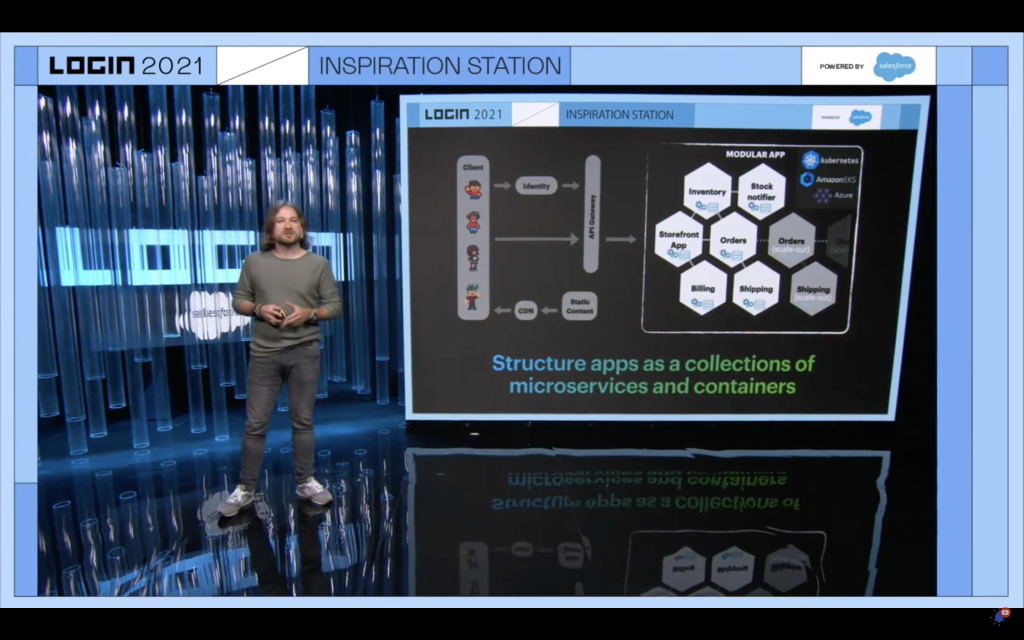
The first step is an in-depth cyber security assessment, using state-of-the-art vulnerability detection and breach simulation practices, and making security part of everyday work by adopting DevSecOps practices.
What is DevSecOps?
DevSecOps – short for “development, security and operations” – is a practice that integrates security measures into every stage of application development: from initial architecture design and coding to testing, deployment and go-live. This differs from classic application development, where security is considered only when the application is ready for production or, worse, when the first user shouts about a problem. In the classic approach security is left to separate security testing or quality assurance (QA) teams, while in DevSecOps security is the responsibility of every developer, DevOps engineer and administrator. Read more about our DevOps services.

You have every tool you need to really test your live systems and improve them.
Cyber security testing in a modern organisation cannot be limited to routine automated vulnerability scanning and printing a standard report full of false positives and real vulnerabilities.
Modern cyber security assessments are carried out in several stages: from standard vulnerability identification, penetration testing, source code audits and social engineering (human vulnerability) testing to staff security training and other activities that assess the organisation’s ability to withstand cyber attacks – and help management sleep more soundly.
In these assessments, the cloud infrastructure and the applications themselves are attacked the way typical modern hackers would do it. To stay rational and assess risk realistically, testers must get to know the business environment and specifics of the organisation being tested, aiming to find the real and most likely business vulnerabilities and weak spots. Sometimes this even means physically posing as an attacker, turning up at the organisation’s office or trying to collect “someone else’s” parcel. Finally, instead of handing over long lists of vulnerabilities and problems for the client to fix alone, all security gaps are closed together.
Once testing is complete, security monitoring components must be put in place.
Top cloud security risks for applications
Some of the most common risks for applications running in the cloud:
- Account takeover due to improper or insufficient access management;
- Data interception and leakage;
- Data loss (losing access to business-critical information);
- Insecure application programming interfaces (APIs);
- Inadequate configuration of cloud infrastructure and storage;
- DDoS attacks.
It is worth noting that Gartner predicts that by 2025 almost all (99%) cloud security failures will be the fault of the organisation using the cloud services.
People become the biggest gap
The human factor must not be forgotten either. In modern organisations, attacks target specific individuals, who often use more than one device in their daily work. Employees are attacked using social engineering scenarios, because people are always more inclined to trust than to check.
Social engineering is the manipulation of people and their minds to bypass information security systems. Technical security measures keep improving, but people do not change. With their weaknesses, stereotypes and biases, they remain the weakest link in information security.
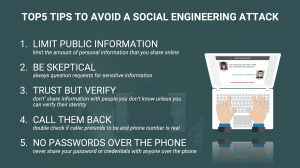
That is why organisations that want to ensure – or raise – an adequate level of security must invest both in security solutions and in people. After all, why hide the safe’s code so carefully if we leave the safe unlocked?
Skaylink (then BTT Cloud) is a leader in managed cloud and IT services in the Baltics. You can raise your security level by testing your infrastructure, monitoring it continuously and making proper use of the software you already have.
More:
For workplace security – BTT Armour
